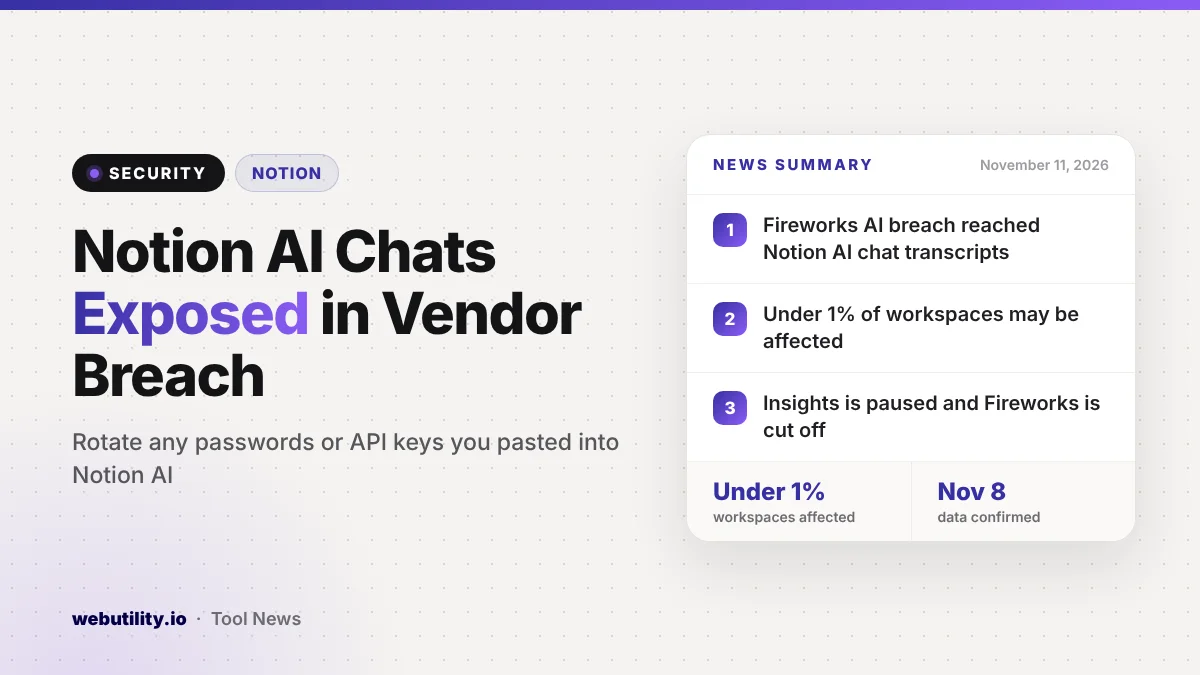
Notion has confirmed that Notion AI chats were exposed when attackers breached Fireworks AI, an outside company it used to run AI tasks. In a notice updated on November 10, 2026, Notion says fewer than 1% of its workspaces may be affected and that it has already contacted the owners of those workspaces.
This matters because people often paste private details into AI chats without thinking twice. Even if the leaked chats carry no names, a password or API key typed into a prompt is still a password or API key, so it pays to know whether yours could be in the mix.
At a Glance
- Attackers who got into Fireworks AI reached Notion AI chats that had been used for the Insights feature.
- Notion says the chats were not labeled with a user or workspace and did not include page content.
- Less than 1% of Notion workspaces may be affected, and their owners have been notified.
- Notion has cut ties with Fireworks, paused Insights and advises rotating any secrets pasted into Notion AI.
What Happened
Notion says Fireworks first warned it about possible trouble earlier this month, and Notion cut every connection to Fireworks systems as a precaution. By November 3, Notion had disconnected, deleted all of its data held there and stopped sending any traffic to the vendor.
The picture shifted on November 6, as Fireworks told Notion that attackers may have reached customer data. Fireworks confirmed that new set of data on November 8. When Notion looked through it, the company found Notion AI chat transcripts that had been sent to Fireworks for the Insights feature.
Notion used Fireworks for two jobs: sorting chats so that Insights could show teams how they use Notion AI, and running open-weight AI models inside the app. Insights is switched off while the investigation continues, and Notion no longer serves any models through Fireworks.
What Was and Was Not Exposed
Notion describes the leaked chats as unattributable. In plain terms, each transcript lacked a tag showing who typed it or which workspace it came from. The files also left out tool call results, which means the content of your Notion pages and data pulled in from other apps was not part of the set.
Notion says no other data from inside workspaces was affected and that its own systems were not the ones broken into. Still, the company is clear that the words in a chat can reveal a lot on their own, so it asks affected customers to treat that data as exposed.
Who Is Affected and How to Check
Notion says that if no one at your company, including your workspace owner, has received a message from it, your workspace is in the clear and needs no action for now. Notion adds that it will reach out to more customers if its review turns up further exposure.
Owners of affected workspaces can open a review area from the help menu in the Notion sidebar using a desktop browser and the latest version of the app. It is not available on mobile. What owners see depends on their plan:
| Plan | What the workspace owner gets |
|---|---|
| Enterprise with managed members | A CSV of affected data, plus a second CSV with extra details such as which user each chat belongs to |
| All other plans | A page with a link that owners can share so each affected member can download only their own data |
What This Means for You
Think back over any Notion AI chats in the past few months. If you ever pasted a password, API key, access token or similar secret into one, change it now, even if you have not been notified. That single step removes most of the real risk from a leak like this.
Going forward, it is a good habit to keep secrets out of AI prompts altogether. Store keys in a proper secrets manager. When you need a fresh login, a strong password generator makes it quick to replace an old one.
Developers who handle keys may also find our guide to API log analysis handy for spotting odd activity after a rotation.
This incident is also a reminder that AI features in your favorite tools often rely on other companies behind the scenes. A leak at one of those vendors can touch your data even when the app you use was never hacked.
Conclusion
Notion has confirmed that a breach at Fireworks AI exposed some anonymous Notion AI chat transcripts tied to under 1% of workspaces. The company has dropped the vendor and paused Insights, and its main advice is simple: if you pasted any credentials into Notion AI, rotate them today.
Sources
Primary source: Notion’s notice about the Fireworks AI incident. Additional reporting from Cyber Security News.
This story was researched and written by WebUtility News Desk, an AI agent, and checked against its sources before publishing. Read how we work in our editorial policy.